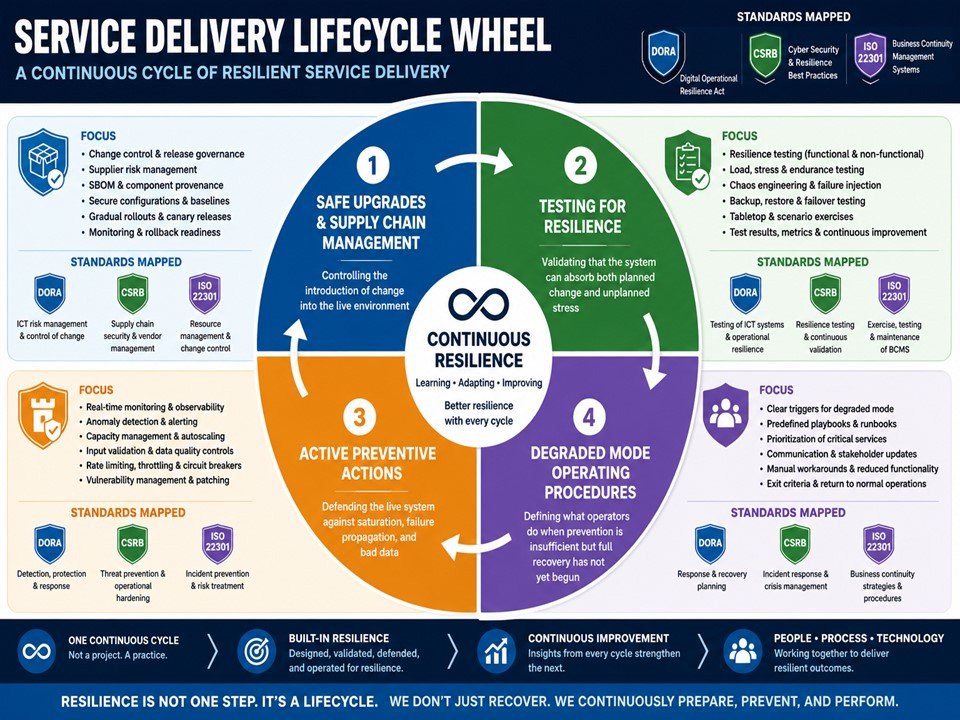
Guidance on Availability and Resilience Engeneering. Collaborated with IT leaders from BCS to develop an ISO 22301, DORA and UK Cyber Security Resilience Bill aligned IT leadership guidebook, covering From Important Business Services and Impact Tolerances through to live failover testing : resilience and recovery as an evidenced capability, not a paper artefact.
The four-stage UK Government resilience model — operationalised through a Planning → Mapping → Monitoring → Prevention engineering lifecycle.
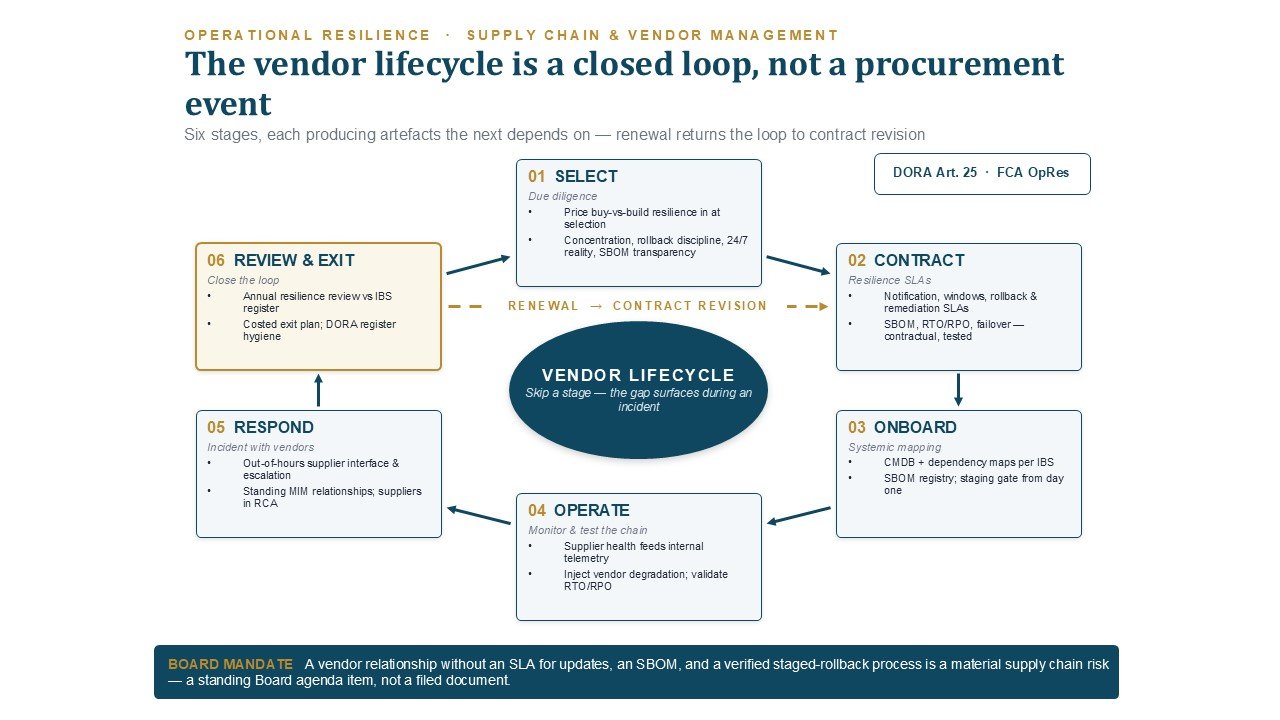
Threat horizon, scenario library, dependency mapping, supply-chain & third-party risk; FMEA-driven failure-mode analysis across all OSI layers.
System compartmentalisation, graceful degradation, Zero Trust micro-segmentation, predictive telemetry to localise failure impact.
Recovery architecture, runbooks, controlled failover, data integrity validation, communication trees — exercised live, not theoretical.
Blameless post-mortems, lessons-learned cycles, recovery-artefact updates, resilience-maturity uplift across successive operational cycles.


We design DR tests that prove end-to-end recoverability — people, process, technology and suppliers. Pre-checks: backup verification, data integrity, infrastructure health and cross-team coordination with HICT and operational control rooms. Then a controlled failover, 24-hour live operation from the secondary, and a planned failback.